Zai Payments offers 3D Secure version 2 (3DS2) on online card payments. This article explains what 3DS2 is, how it works, what it does for your business, and how to get started.
Other articles in this series:
- 3DS2: What to expect
- 3DS2: Understanding payment outcomes
- 3DS2: Liability shift and disputes
- 3DS2: Getting the best results and support
What is 3DS2?
3DS2 is the current version of the card schemes' cardholder authentication standard (marketed as Visa Secure, Mastercard Identity Check, and American Express SafeKey). Before a card payment is sent for authorisation, 3DS2 lets the card issuer (your customer's bank) confirm that the person paying is the genuine cardholder.
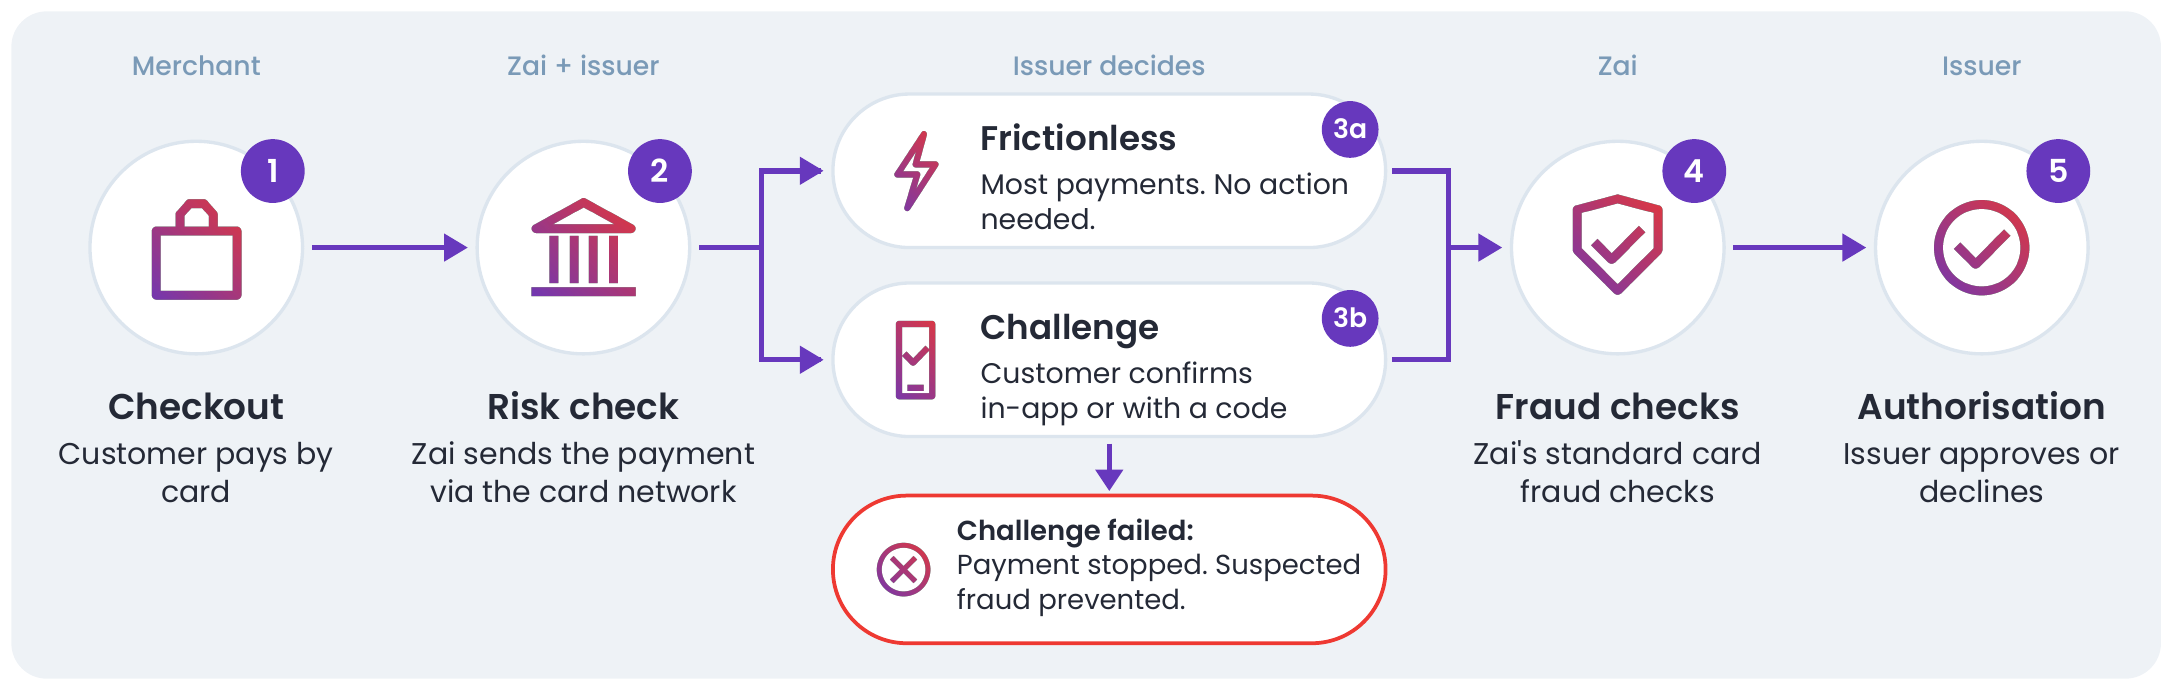
It replaces the older 3DS1, which relied on static passwords and full-page redirects. 3DS2 shares far more data with the issuer, so most payments can be authenticated in the background without the cardholder doing anything. This is known as a "frictionless" authentication.
How does 3DS2 work?
Here is how a 3DS2 payment flows from checkout to approval, and who is involved at each step.
Why would I use 3DS2?
There are two main reasons:
- Fraud protection. Card-not-present (CNP) fraud, such as online or in-app payments made with stolen card details, makes up the large majority of card fraud in Australia. Authentication is the most effective industry tool against it.
- Dispute protection. Successfully authenticated transactions generally move liability for fraud-related chargebacks from you to the card issuer. See 3DS2: Liability shift and disputes.
What do I get from 3DS2?
- Lower fraud. Fraudsters using stolen card details are far less likely to pass issuer authentication.
- Liability shift. For successfully authenticated transactions, liability for fraud-related chargebacks generally moves to the issuer, so you are not left carrying the loss.
- Fewer disputes and less admin. Fewer fraud chargebacks means less time gathering evidence and responding to disputes.
- Better issuer confidence. Issuers can see richer data about the transaction, which can support approval of genuine payments that might otherwise look unusual.
- Mostly invisible to your customers. Unlike 3DS1, most authentications under 3DS2 are frictionless and need no action from the cardholder.
- Mobile-friendly authentication. Where the bank needs the cardholder to verify the payment (a "challenge"), it is designed for mobile, and many banks use their own app (biometrics or push approval) instead of passwords.
Is 3DS2 turned on for my payments?
Not automatically. 3DS2 needs to be enabled on your Zai account before you can use it. This is a one-time setup step. To request it:
- Existing customers: speak to your Account Manager
- New customers: speak to your Business Development Manager
- Anyone: contact Zai Technical Support at support@zaipayments.com
Once 3DS2 is enabled, your integration determines which payments go through 3DS2. In most cases, using 3DS2 is your choice. However, Zai may require some merchants to use it (see "Can I choose not to use 3DS2?" below).
Is there a cost to use 3DS2?
Please discuss pricing with your Business Development Manager or Account Manager when enabling the service.
Is Zai's 3DS2 service certified?
Yes. Zai's 3DS solution is certified by our card payments provider, confirming that our implementation meets the 3DS2 specification and works correctly with the card schemes and issuers.
Can I choose not to use 3DS2?
In most cases, yes. However, Zai may require you to use 3DS2, depending on your business model and risk profile. If this applies to your business, we will let you know during onboarding or when your risk profile changes, and explain what is required.
Where 3DS2 is optional and you choose not to use it, keep in mind that:
- You will not benefit from the liability shift on fraud-related chargebacks
- Your exposure to CNP fraud may be higher
Does 3DS2 apply to every type of card payment?
No. 3DS2 is designed for customer-initiated online payments where the cardholder is present to authenticate, such as one-off online payments and the first payment when a card is stored for future use.
Merchant-initiated transactions (MITs), such as subsequent recurring or instalment payments using a stored card, are typically out of scope.
Do my existing stored cards need to be re-authenticated?
No. Cards you have already stored with Zai do not need to be re-authenticated with 3DS2.
Glossary
- 3DS2: 3D Secure 2, the card schemes' cardholder authentication standard
- ACS (Access Control Server): the issuer's system that decides how to authenticate the cardholder
- Challenge: a step where the cardholder actively verifies their identity
- CNP: card-not-present, for example online or in-app payments
- Frictionless: authentication completed in the background with no cardholder action
- Issuer: the bank or institution that issued the card
- Liability shift: the transfer of fraud chargeback liability from merchant to issuer for authenticated transactions
- MIT: merchant-initiated transaction, such as a scheduled recurring payment
Need help? Contact Zai Technical Support at support@zaipayments.com. To help us investigate quickly, see what to include in 3DS2: Getting the best results and support.
Was this article helpful?
That’s Great!
Thank you for your feedback
Sorry! We couldn't be helpful
Thank you for your feedback
Feedback sent
We appreciate your effort and will try to fix the article